AI finds bugs faster. The patch still needs an owner.
· re: Updating our coordinated vulnerability disclosure policy timelines (Anthropic)
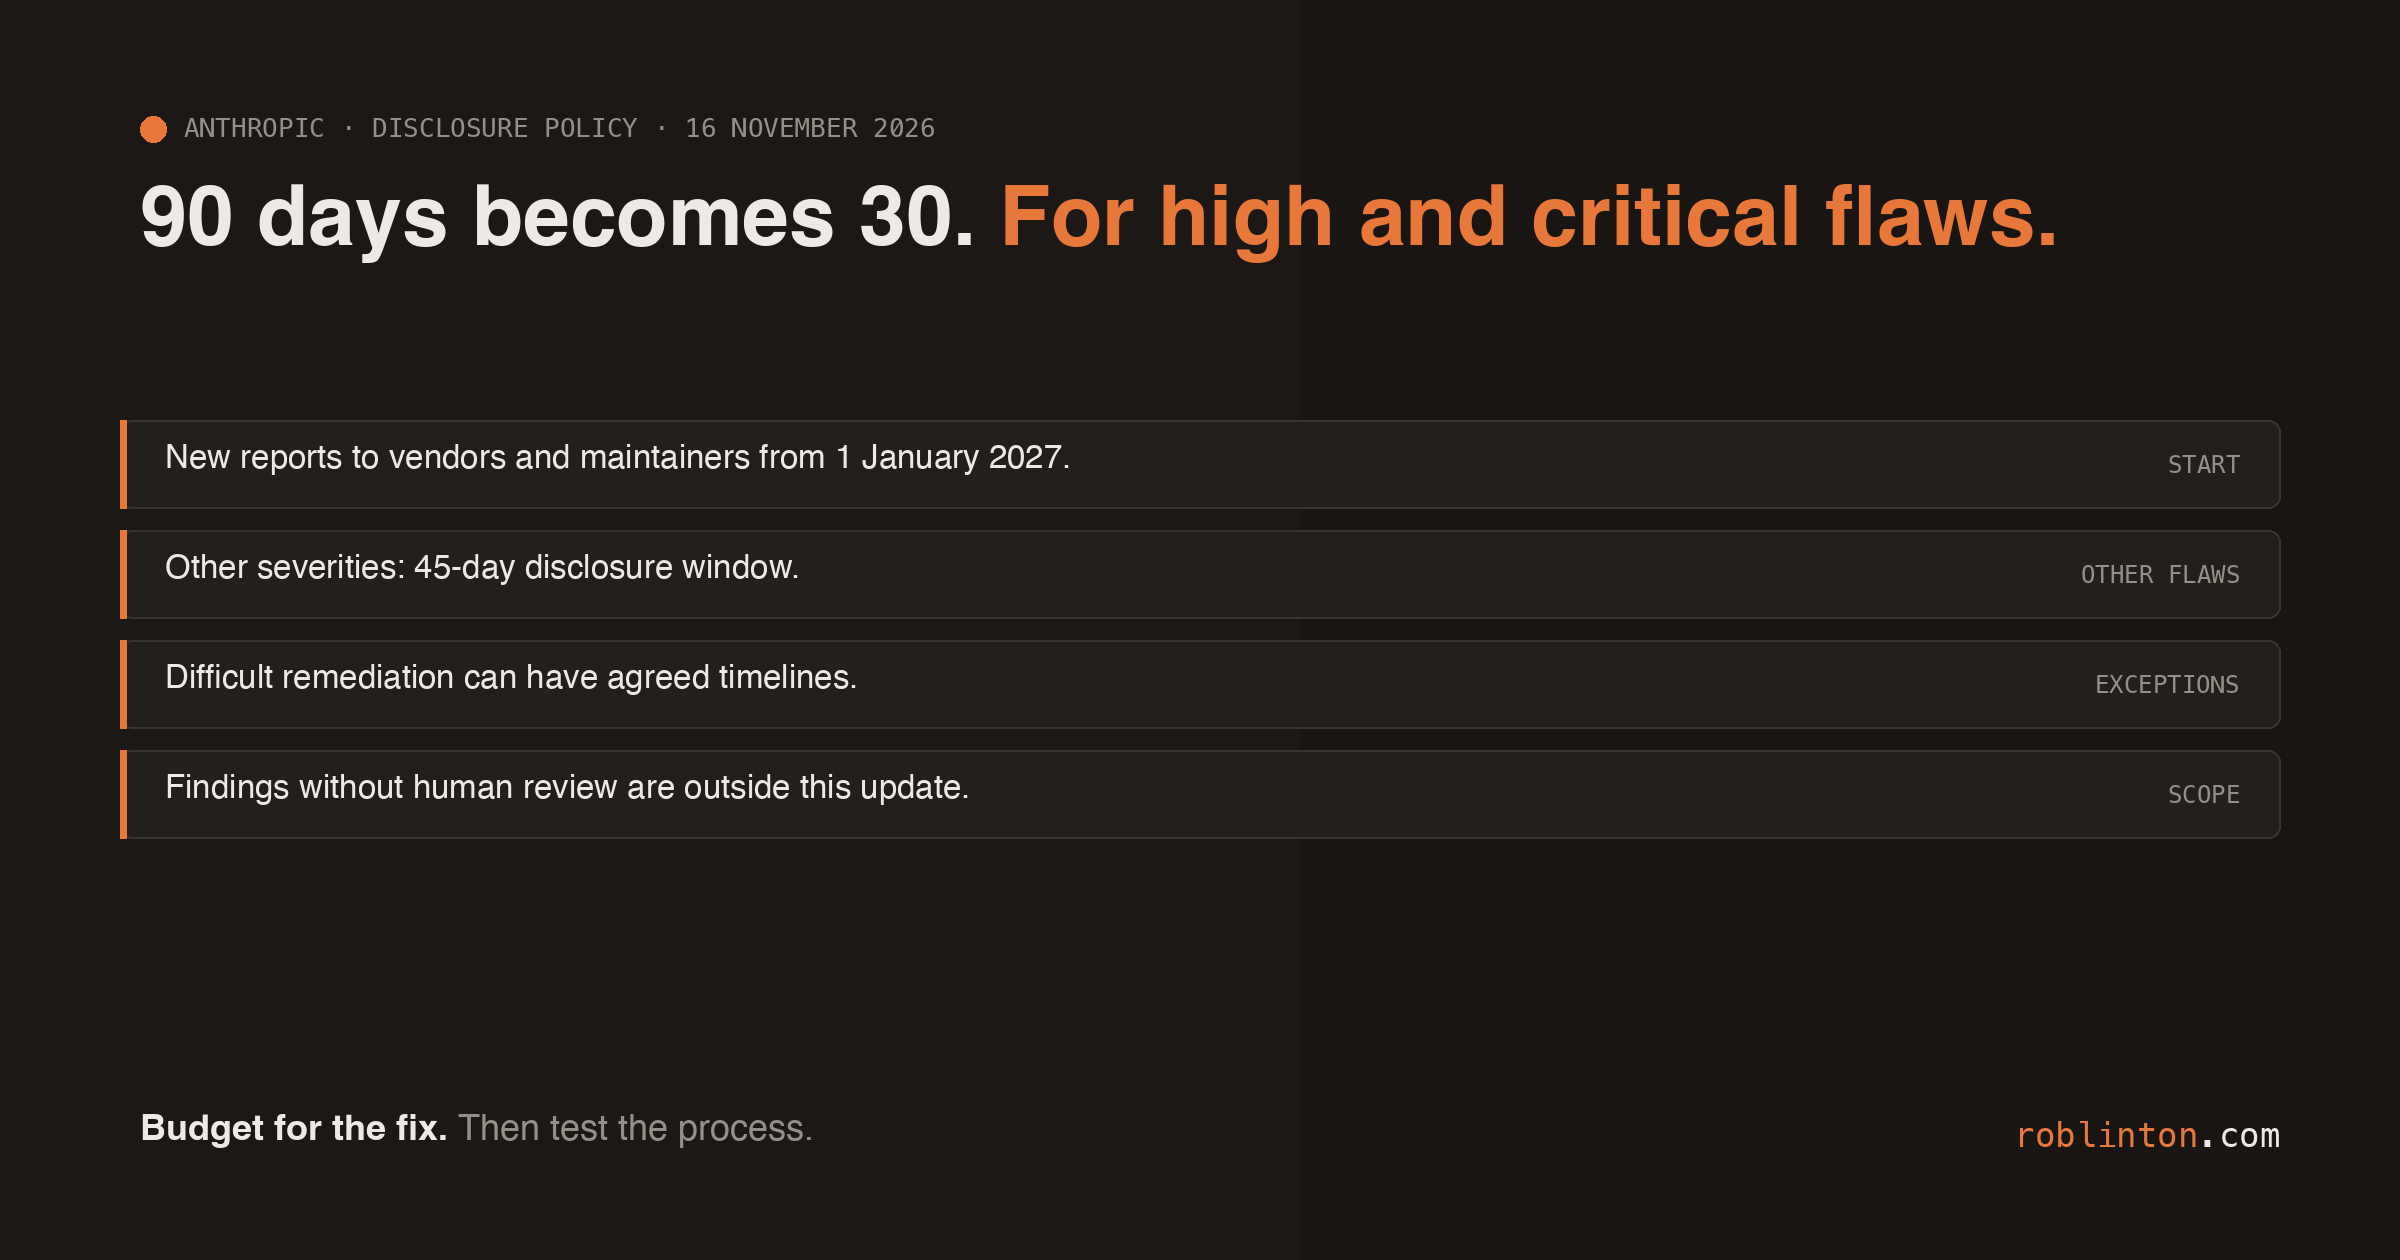
Faster vulnerability discovery needs a faster way to ship the fix.
Anthropic’s 16 November policy update cuts its disclosure window from 90 days to 30 for high and critical flaws, and 45 for others. Those windows apply to vulnerabilities it reports to vendors and maintainers from 1 January 2027.
(The change advisory board has not acquired a GPU.)
Anthropic says models are increasingly rediscovering the same bugs, so it no longer expects a finding to stay private for three months. It still allows different remediation timelines for difficult cases, including critical infrastructure. Findings without human review are outside this update.
My read: the useful AI security investment includes the dull bit after discovery. Have someone who receives the report, can reproduce it and can get a tested fix into production. Funding another scanner while leaving that queue understaffed is an odd way to reduce exposure.
For teams receiving these reports, January is a sensible deadline to check the process. Time the route from the security inbox to a tested fix ready for release. If the report spends most of its life waiting for the next meeting, start there.