Denmark's biggest ID breach was caught by the invoice
· re: Omfattende uautoriseret adgang til borgeres CPR-oplysninger (Danish Ministry of Research, Education and Digitalisation)
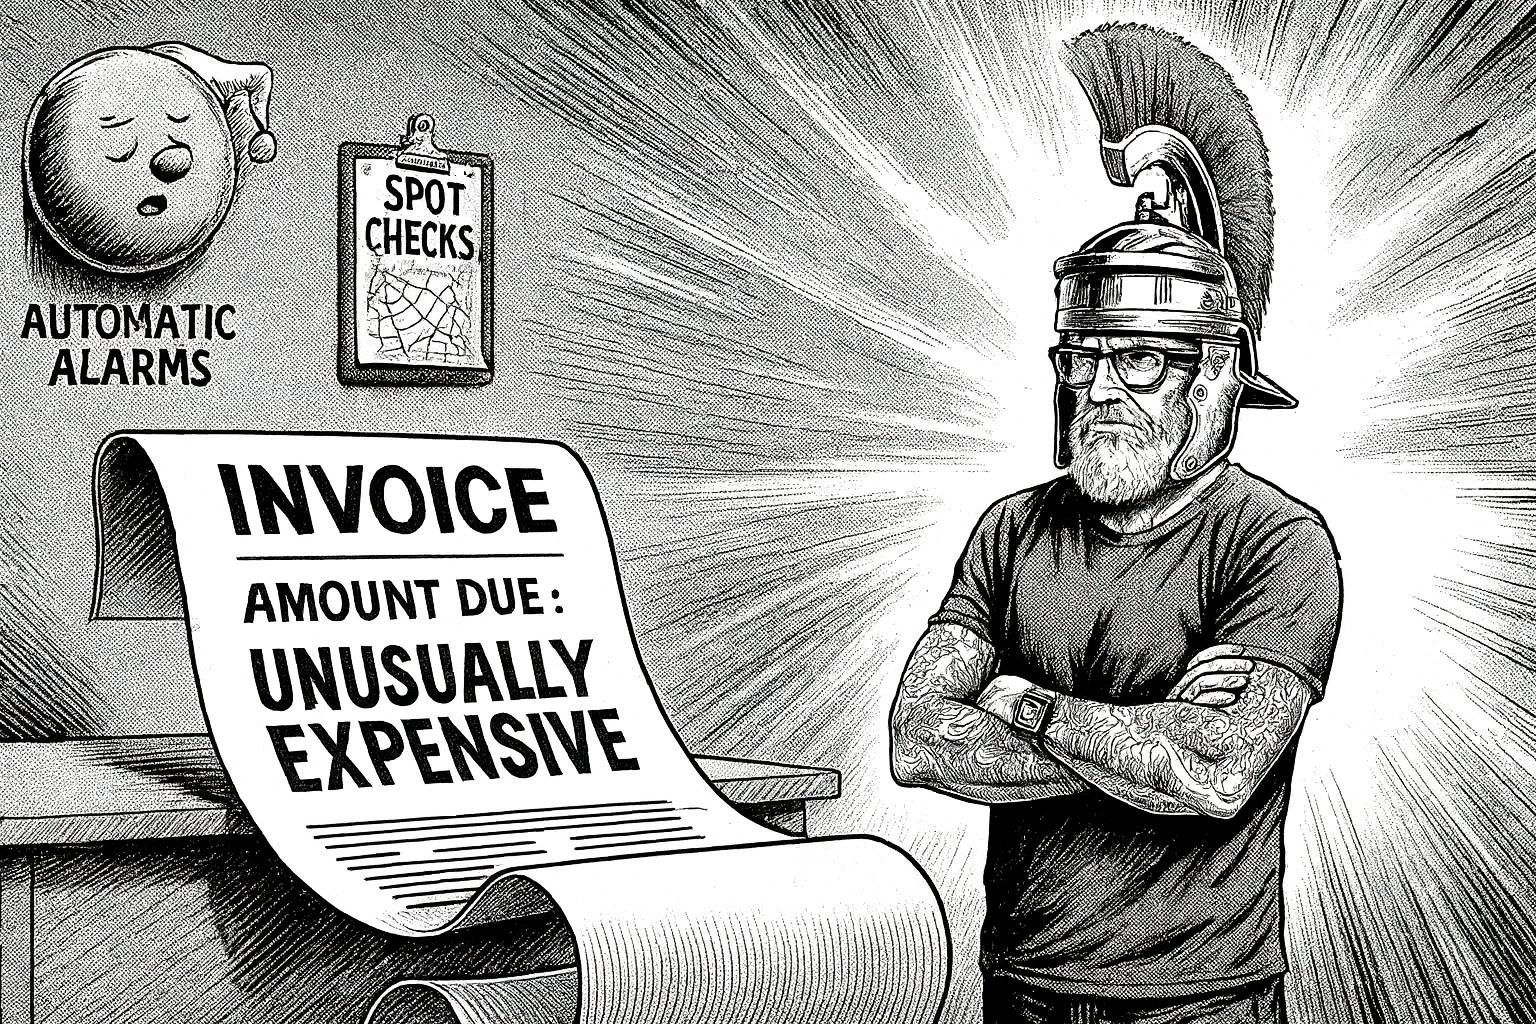
Denmark has found the one intrusion detection system nobody ever switches off. Billing.
On 5 October the Danish digitalisation ministry said attackers had got names, addresses and CPR numbers (the national ID number) for about 8.8 million registered people, “by misusing a Danish company’s lawful access to search for information in the CPR system”. (My translations, here and below.) The 8.8 million includes people who have died or emigrated, so it is a bigger number than Denmark has residents.
DR’s account of how it was found: “It was neither automatic alarms nor spot checks” that caught it. It was “the unusually expensive bill” issued to “a smaller company” at the end of September. (Somebody in billing deserves a raise.)
My read: the access was lawful on paper, so access control apparently had nothing to object to. The thing that did notice was, I suspect, whatever bills by usage.
Net: if your invoice is better at spotting abuse than your monitoring, move the invoice logic into the monitoring. Volume is a signal.