Dropbox breach needed no password, just an email address
· re: Dropbox says 5,000 accounts were breached through a Lenovo ID flaw (The Next Web)
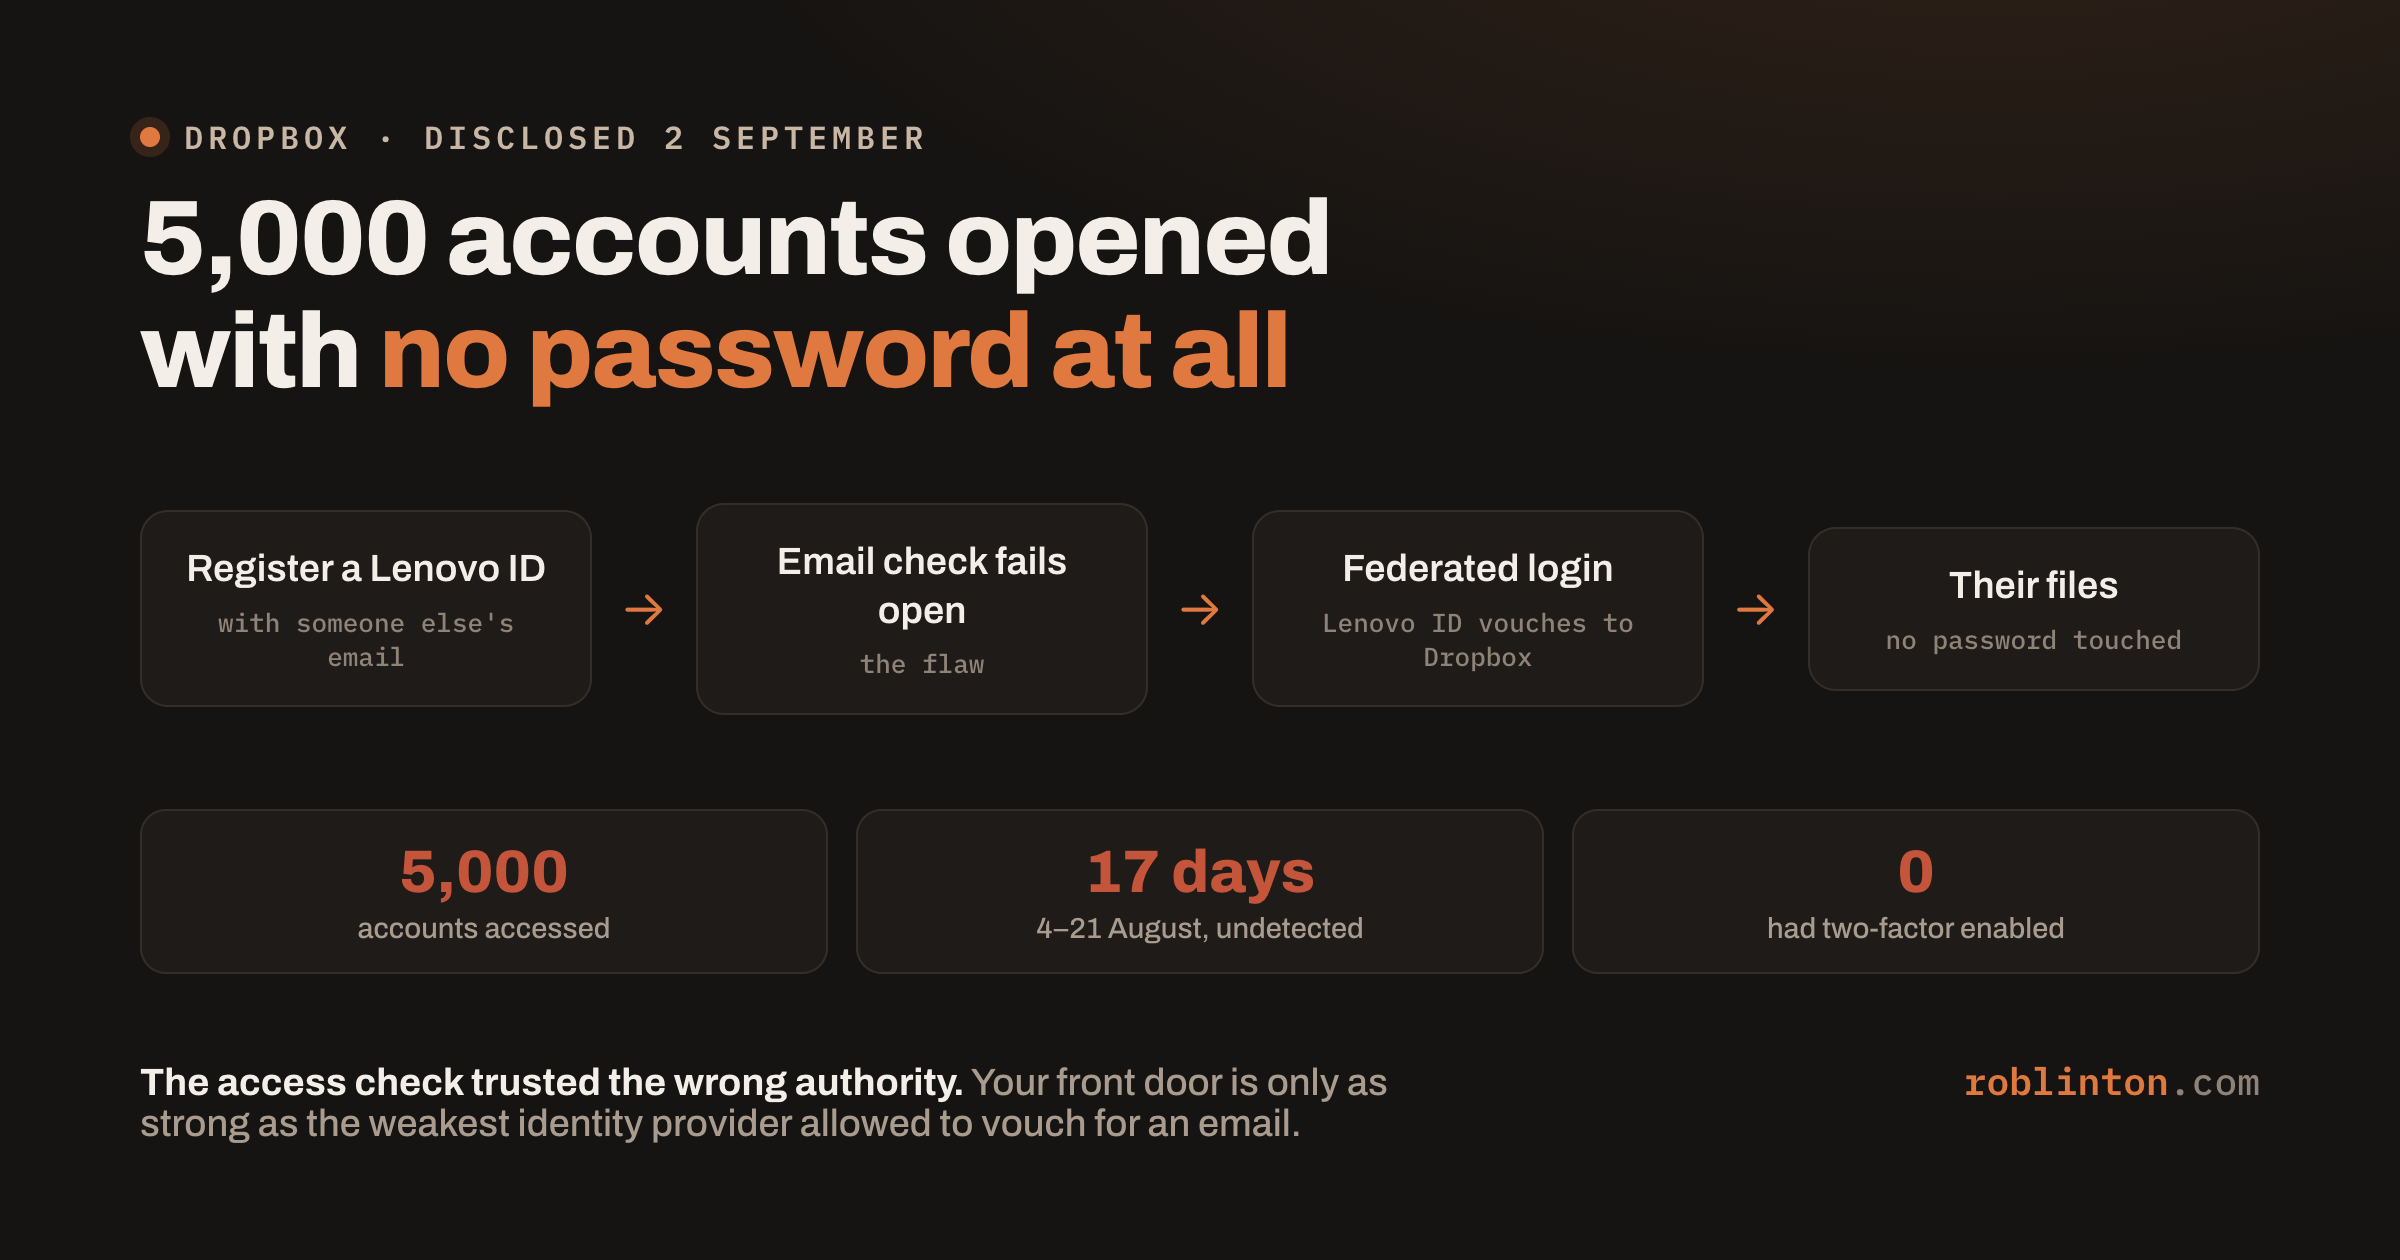
Dropbox disclosed this week that 5,000 accounts were accessed between 4 and 21 August 2026 with no password involved at any point. The attacker registered a Lenovo ID using someone else’s email address, a legacy email-verification flaw let it stand, and the federated login walked straight into the Dropbox account attached to that email. Seventeen days before it was caught. Every compromised account lacked two-factor. The numbers here all come via The Next Web’s report of the disclosure; I have not read Dropbox’s own notice.
My read: this is not a password story, it is a delegation story. Federated identity means your front door accepts vouchers, and a voucher system is only as strong as the weakest issuer allowed to vouch. Dropbox’s own checks apparently never failed; they trusted an authority whose checks did. If you have single sign-on integrations from years back still wired to production, this is what they look like when they age.
The part I would put on a slide: the fix here was never stronger passwords, because no password was used. The two controls that mattered were refusing to link a federated login to an existing account on an email match the issuer never verified, and a second factor. (Credit where due: files were viewed in fewer than a third of the accounts, per the disclosure, and Dropbox said that plainly, from logs.)
I made my own bet on this problem in 2012 with Podzy, an encrypted, fully on-premise alternative to Dropbox, so I have opinions about where file-store trust should live; the product ones stay off this note. The general lesson stands anywhere: an identity check is only as good as the authority behind it, and the check has to happen where the data is. A partner’s door can stand open for seventeen days before anyone notices.