Four in five people in DTU's breached system had already left
· re: Cyberattack on DTU: notification of a personal data breach (Technical University of Denmark (DTU))
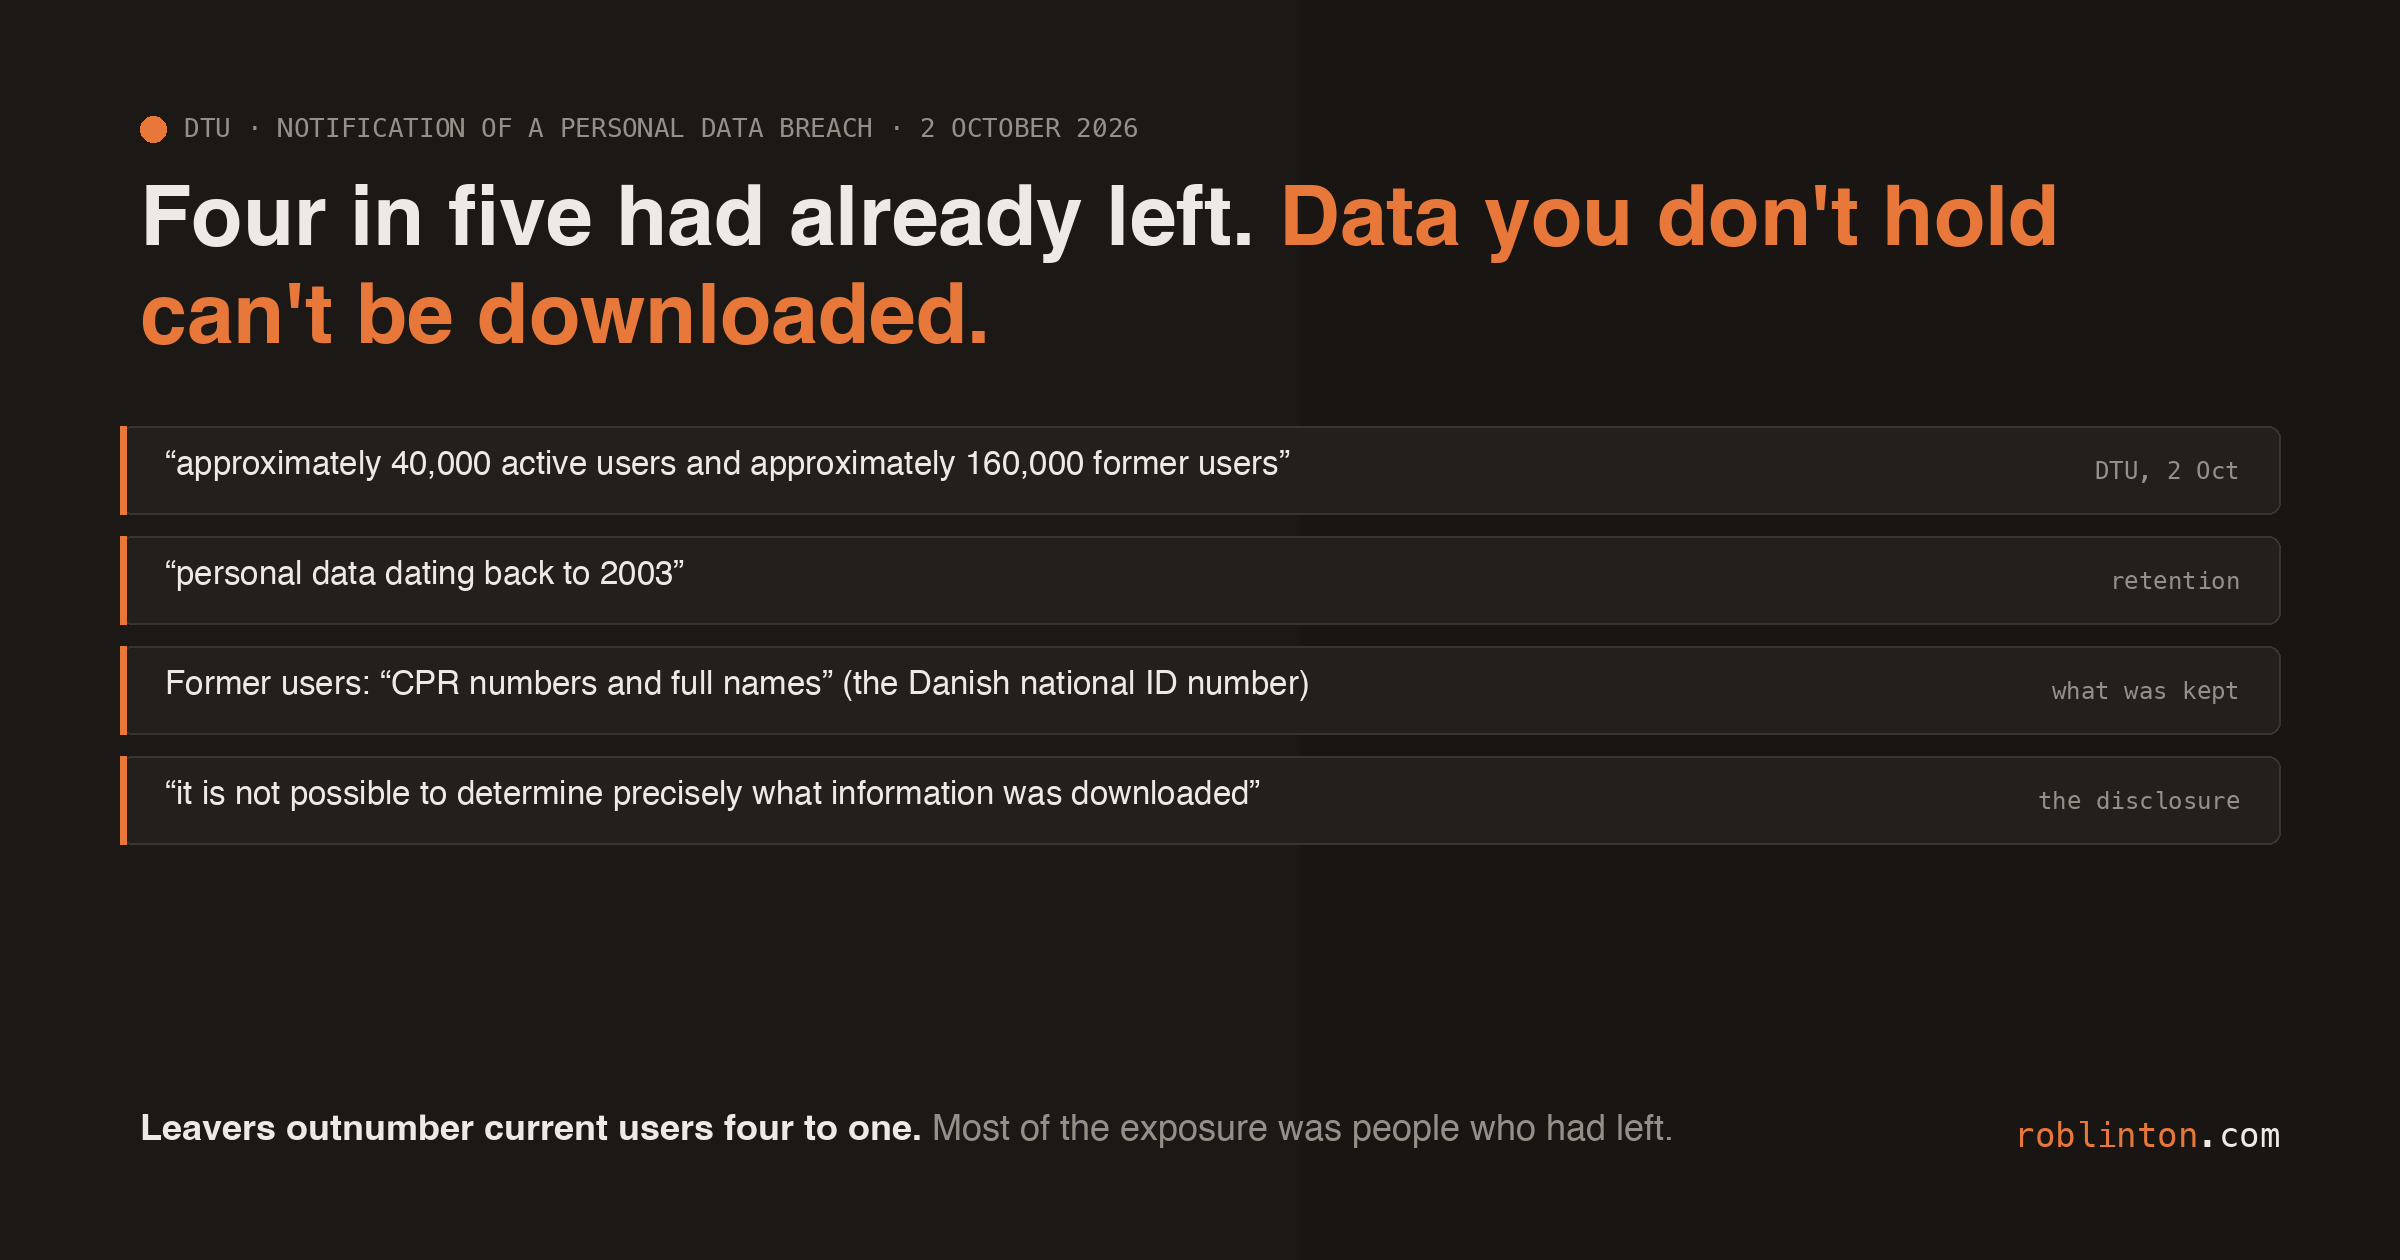
Four in five of the people in the system DTU’s attackers got into weren’t there any more. The Technical University of Denmark disclosed on Friday that attackers “downloaded a large amount of data” from DTUBasen, its identity and access management system. The count: “approximately 40,000 active users and approximately 160,000 former users”, with “personal data dating back to 2003”.
For former users that still includes “CPR numbers and full names”. The CPR is the Danish national ID number, so not a password anyone can reset. In fairness, DTU did delete former users’ addresses and photos after six months. Somebody thought about it. They just stopped short of the field that mattered.
Then the line every incident team will recognise: “it is not possible to determine precisely what information was downloaded or how many people have been affected.” (Regular readers know why I keep banging on about logging every read.)
My read: an identity system is for people who need access today. Keep a national ID number for someone who left years ago and it’s an archive with a login page. (There may well be a legal reason to keep a CPR against a degree record. Fine, but that’s an archive’s job, not the login system’s.)
Net: go and count the leavers in your own directory. Whatever you still hold on them is what you’d be disclosing.