Stolen email finally got a data residency policy
· re: Chinese Government-linked Cyber Threat Actors Combine Automated and Hands-on Hacking Tools to Steal Sensitive Data (AA26-281A) (FBI, CISA, NSA, NCSC-UK, ASD's ACSC and partners)
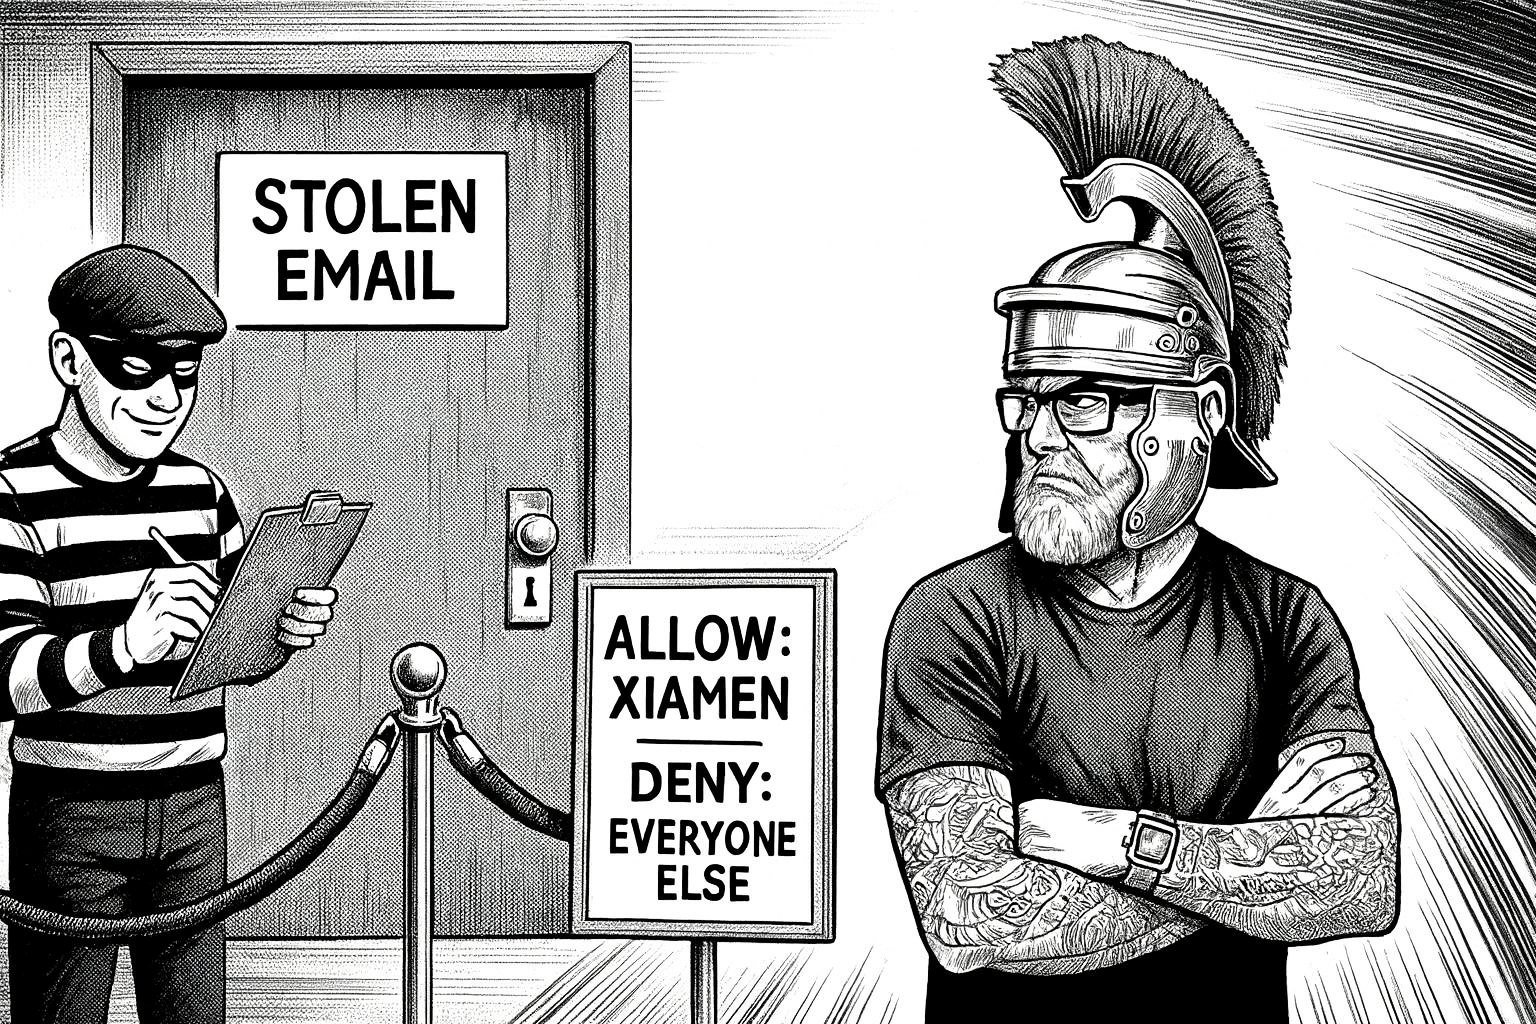
The best data residency control I read about this week was run by the people who stole the data.
A joint advisory published on 8 October (FBI, CISA, NSA, the UK’s NCSC, our own ASD’s ACSC and five others) describes “Chinese government-linked cyber threat actors” taking email from “government organizations, law enforcement agencies, healthcare systems, and religious institutions located in Southeast Asia”. Then this, in the advisory’s flat voice: “In some instances, the threat actors restricted access to the exfiltrated data to only IP addresses from Xiamen, China.”
Once stolen, the mail finally got an allowlist and a jurisdiction.
My read: where data sits and who can reach it is a decision, not a property of the cloud. The thieves made that decision on purpose. I suspect plenty of us never made it at all.
Net: if a thief can put your data behind a geofence, “it’s in the cloud somewhere” isn’t a residency policy.